Deterministic request firewall and output sanitization. More...
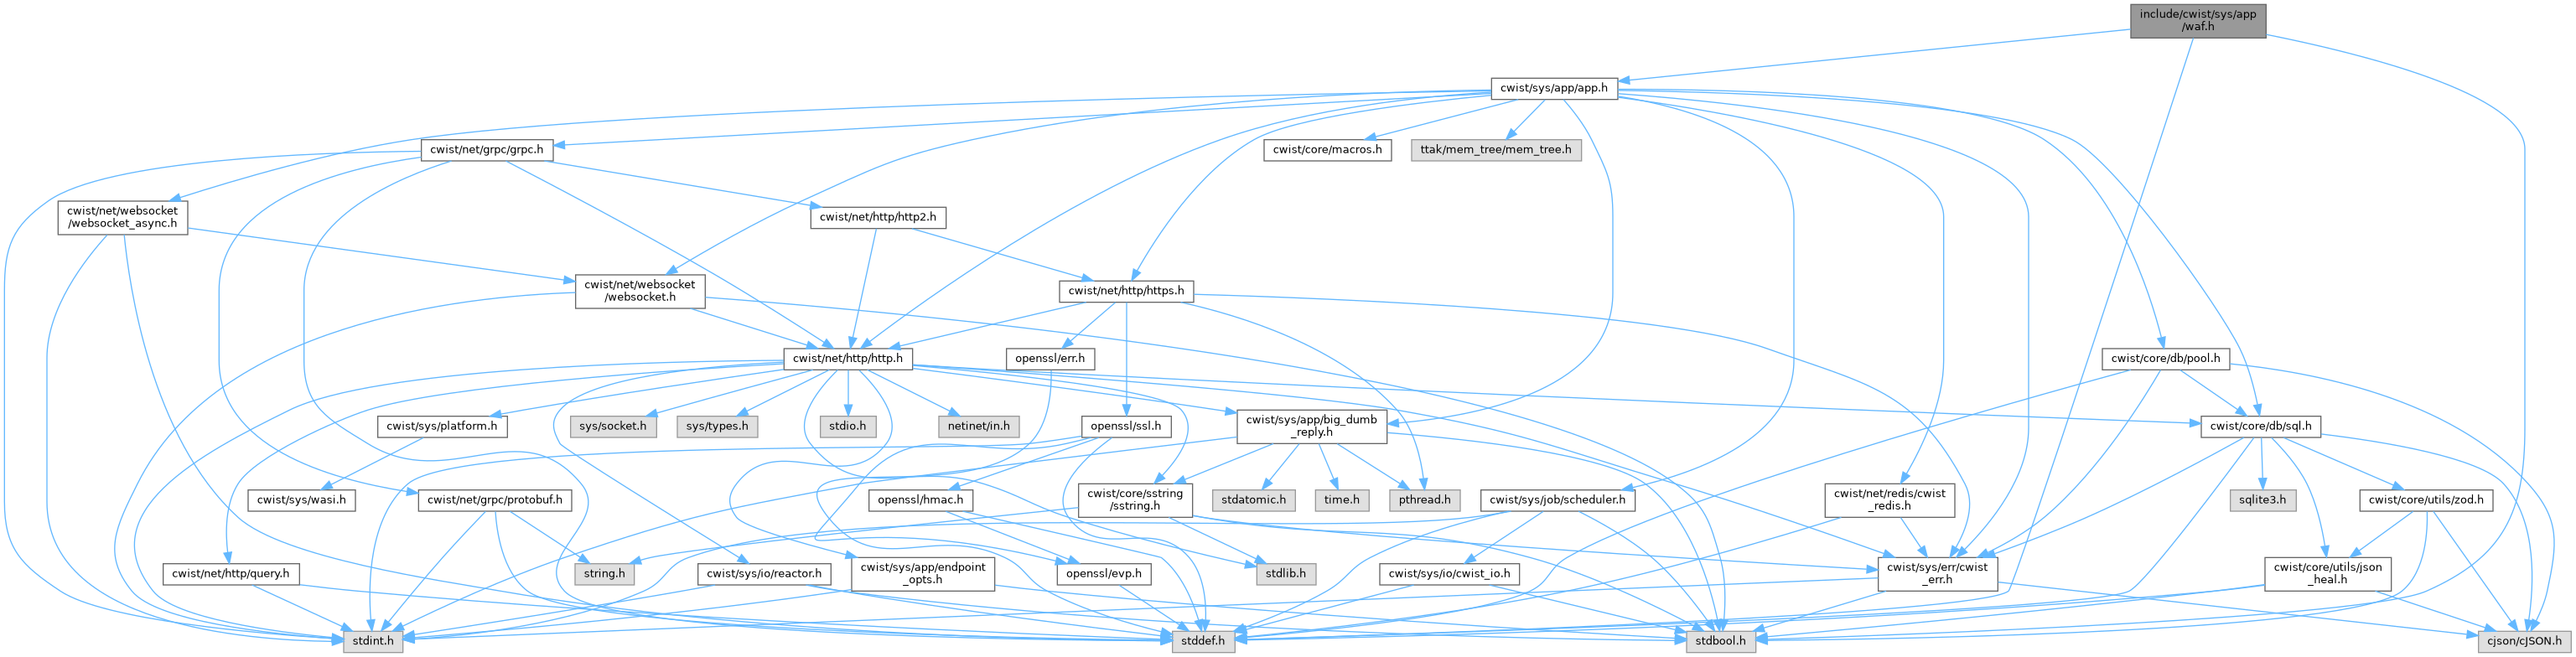
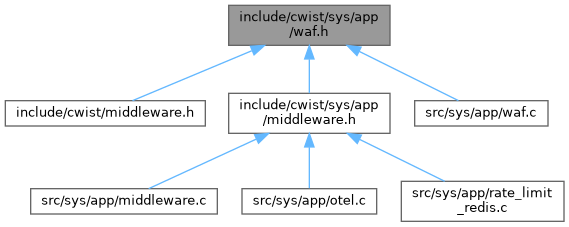
Go to the source code of this file.
Functions | |
| cwist_middleware_func | cwist_mw_waf_lite (void) |
| Construct the WAF-lite middleware. | |
| bool | cwist_waf_is_safe (const char *input, size_t length) |
| Check whether a byte string is free of hostile signatures. | |
| char * | cwist_sanitize_html (const char *input) |
| Escape HTML-special characters in a NUL-terminated string. | |
Detailed Description
Deterministic request firewall and output sanitization.
Definition in file waf.h.
Function Documentation
◆ cwist_mw_waf_lite()
| cwist_middleware_func cwist_mw_waf_lite | ( | void | ) |
◆ cwist_sanitize_html()
Escape HTML-special characters in a NUL-terminated string.
Replaces '&', '<', '>', '"', and '\'' with their HTML entity equivalents and returns a newly allocated buffer holding the escaped text.
- Parameters
-
input Input string; may be NULL.
- Returns
- Newly allocated, NUL-terminated escaped string that the caller owns and must free with cwist_free, or NULL if
inputis NULL, on allocation failure, or on size overflow.
Definition at line 141 of file waf.c.
References cap, and cwist_alloc().
◆ cwist_waf_is_safe()
Check whether a byte string is free of hostile signatures.
Scans input once (O(length)) through the case-insensitive Aho-Corasick automaton, which is built lazily on first call. Matching is ASCII-only: bytes at or above 0x80 reset the automaton state, and control bytes other than tab, newline, and carriage return are rejected outright.
- Parameters
-
input Byte string to scan; may be NULL. length Number of bytes to scan.
- Returns
- true if the input is safe, false if a signature or disallowed control byte is found. NULL input is considered safe.
Definition at line 113 of file waf.c.
References cap, and WAF_ALPHABET.
