Loading...
Searching...
No Matches
#include <cwist/security/tls/ech.h>#include <cwist/sys/err/cwist_err.h>#include <openssl/ssl.h>#include <openssl/opensslv.h>#include <stdio.h>
Include dependency graph for ech.c:
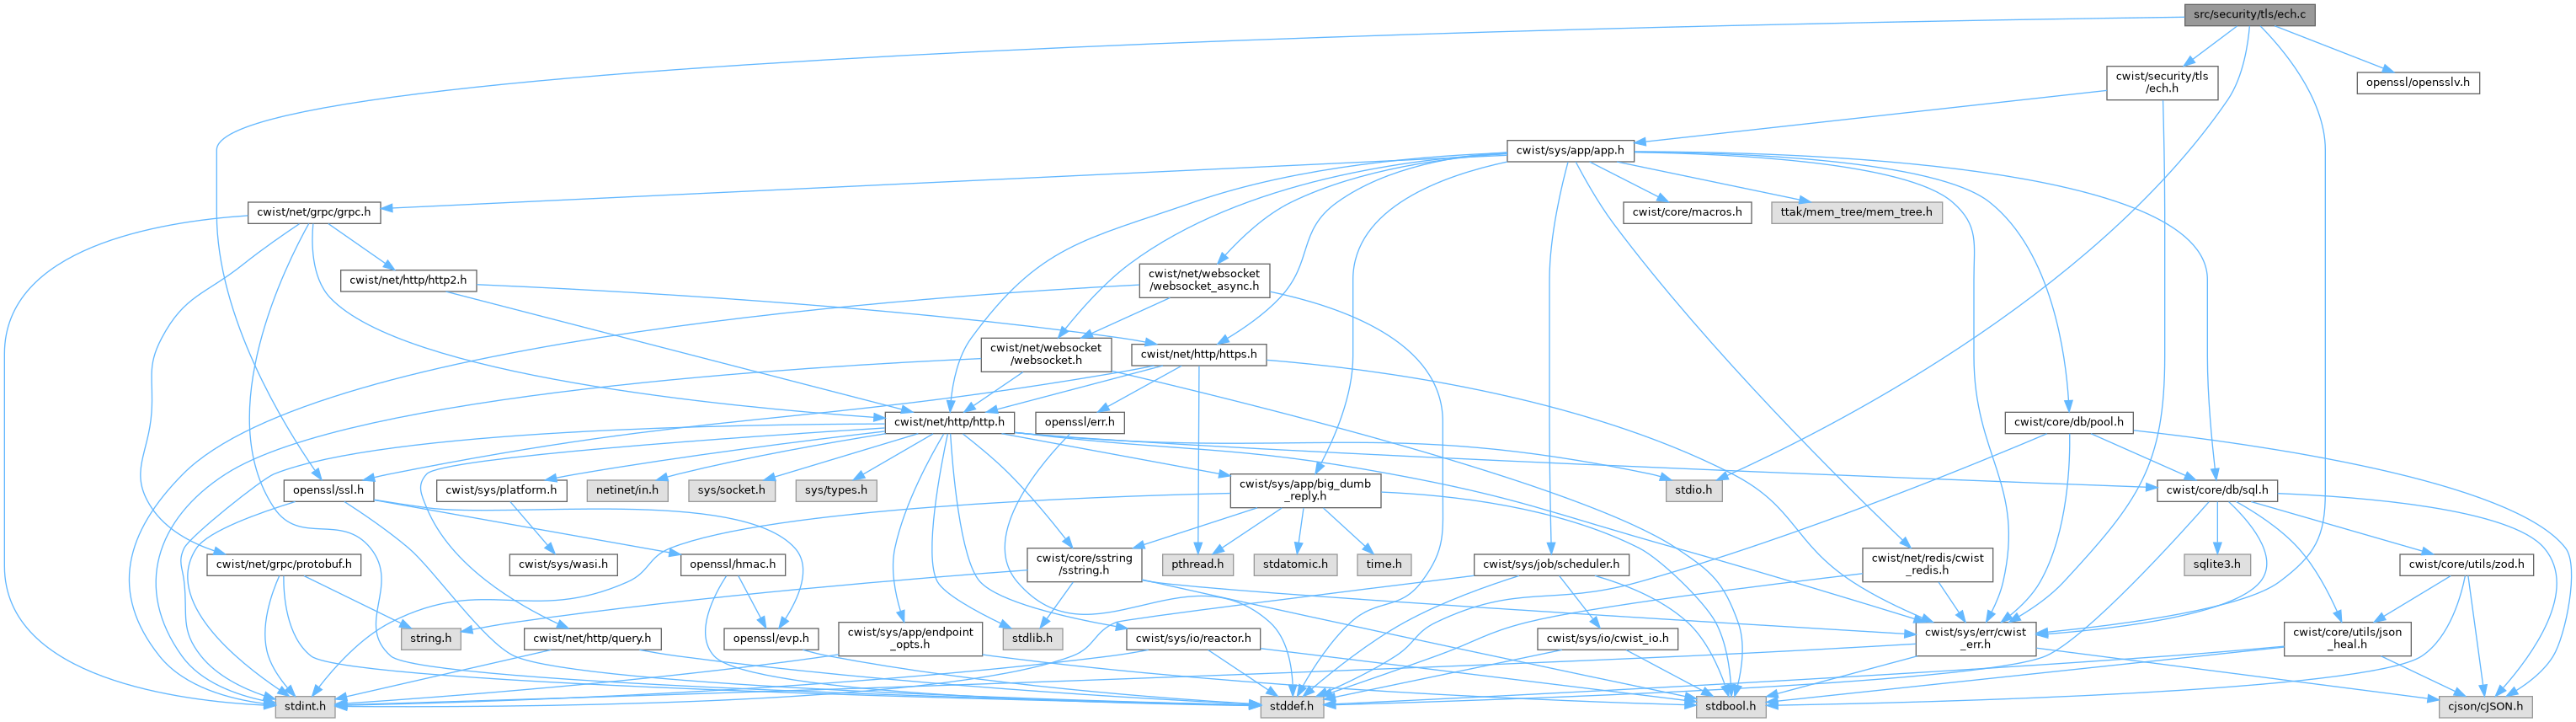
Go to the source code of this file.
Macros | |
| #define | _GNU_SOURCE |
Functions | |
| cwist_error_t | cwist_app_use_ech (cwist_app *app, const char *ech_key, const char *ech_dir) |
| Enable ECH (Encrypted Client Hello) support for an application. | |
Detailed Description
Macro Definition Documentation
◆ _GNU_SOURCE
Function Documentation
◆ cwist_app_use_ech()
Enable ECH (Encrypted Client Hello) support for an application.
Enable Encrypted Client Hello (ECH) for the application.
When built against OpenSSL 3.2 or newer with ECH support (SSL_OP_ENABLE_ECH defined), this sets the ECH option on the application's SSL context. On older OpenSSL versions this is a no-op that still succeeds. The ech_key and ech_dir arguments are currently accepted but not used.
- Parameters
-
app Application whose SSL context is configured. Must not be NULL. ech_key Unused placeholder for a future ECH key configuration. ech_dir Unused placeholder for a future ECH directory source.
- Return values
-
CWIST_ERROR_INVALID_PARAM appis NULL.0 Success; ECH was enabled or is unsupported on this build.
Definition at line 28 of file ech.c.
References cap, cwist_https_context::ctx, CWIST_ERR_INT16, CWIST_ERROR_INVALID_PARAM, make_error(), cwist_app::ssl_ctx, and SSL_CTX_set_options.
