DTLS helpers: ephemeral certificate generation, fingerprint, SSL_CTX. More...
#include "webrtc_internal.h"#include <openssl/ec.h>#include <openssl/evp.h>#include <openssl/x509.h>#include <pthread.h>#include <stdio.h>#include <string.h>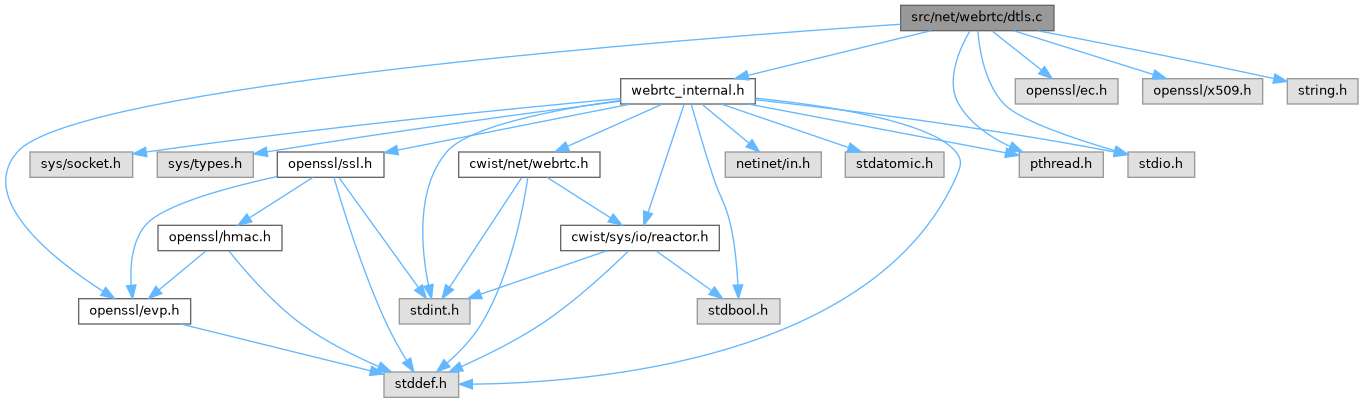
Go to the source code of this file.
Macros | |
| #define | CWIST_DTLS_MTU 1200 |
| DTLS record/link MTU assumed for the media path (bytes). Used to size outgoing DTLS records so they fit typical UDP/ICE paths without IP fragmentation. | |
Functions | |
| int | cwist_dtls_generate_cert (X509 **cert_out, EVP_PKEY **pkey_out) |
| Generate an ephemeral self-signed ECDSA certificate for DTLS. | |
| int | cwist_dtls_fingerprint (X509 *cert, char *out, size_t cap) |
| Compute the SHA-256 fingerprint of a certificate in SDP format. | |
| SSL_CTX * | cwist_dtls_ctx_new (int is_server, X509 *cert, EVP_PKEY *pkey) |
| Create a DTLS SSL_CTX for the client or server role. | |
| unsigned int | cwist_dtls_link_mtu (void) |
| Return the DTLS link MTU in bytes. | |
| BIO * | cwist_dtls_bio_new (struct cwist_webrtc_conn *conn) |
Datagram BIO for conn: reads return conn->dtls_in once, writes go to cwist_webrtc_conn_dtls_out() one datagram per call. | |
Detailed Description
DTLS helpers: ephemeral certificate generation, fingerprint, SSL_CTX.
Provides the minimal DTLS layer for WebRTC: an ephemeral self-signed ECDSA certificate, the SHA-256 certificate fingerprint used in SDP a=fingerprint attributes, construction of client/server SSL_CTX objects pinned to DTLS 1.2, and the datagram BIO the sessions run on.
Definition in file dtls.c.
Macro Definition Documentation
◆ CWIST_DTLS_MTU
| #define CWIST_DTLS_MTU 1200 |
Function Documentation
◆ cwist_dtls_bio_new()
| BIO * cwist_dtls_bio_new | ( | struct cwist_webrtc_conn * | conn | ) |
Datagram BIO for conn: reads return conn->dtls_in once, writes go to cwist_webrtc_conn_dtls_out() one datagram per call.
Definition at line 211 of file dtls.c.
References cap.
◆ cwist_dtls_ctx_new()
Create a DTLS SSL_CTX for the client or server role.
DTLS 1.2 SSL_CTX for the server (with cert) or client role.
- Parameters
-
is_server Non-zero to build a DTLS server context, zero for a DTLS client context. cert Server certificate; used (with pkey) only whenis_serveris non-zero. May be NULL for a client.pkey Private key matching cert; only used for a server.
- Returns
- New SSL_CTX on success, NULL on allocation failure or when certificate/key loading or validation fails on the server side.
- Note
- The context is pinned to DTLS 1.2 as the minimum protocol version. Client contexts use SSL_VERIFY_NONE: peer fingerprint verification is deferred to the SDP exchange (the test pins the expected fingerprint out of band).
Definition at line 120 of file dtls.c.
References cap, SSL_CTX_check_private_key, SSL_CTX_free, SSL_CTX_new, SSL_CTX_set_min_proto_version, SSL_CTX_set_verify, and SSL_VERIFY_NONE.
◆ cwist_dtls_fingerprint()
Compute the SHA-256 fingerprint of a certificate in SDP format.
SHA-256 fingerprint of cert in SDP form ("AB:CD:...").
- Parameters
-
cert Certificate to hash; must be non-NULL. out Output buffer receiving the fingerprint text. cap Capacity of outin bytes (including the NUL terminator).
- Returns
- 0 on success, -1 if the DER encoding fails, the certificate exceeds the internal 2048-byte DER buffer, or the digest does not fit in
out.
- Return values
-
0 Fingerprint written, e.g. "AB:12:...:EF" in uppercase hex. -1 Encoding, size, or digest error.
- Note
- The result is the colon-separated uppercase hex SHA-256 digest as used in the SDP a=fingerprint attribute. No terminator is written beyond what snprintf() already emits.
Definition at line 90 of file dtls.c.
References cap, EVP_MAX_MD_SIZE, and EVP_sha256.
◆ cwist_dtls_generate_cert()
Generate an ephemeral self-signed ECDSA certificate for DTLS.
Generate an ephemeral self-signed P-256 certificate.
- Parameters
-
cert_out Receives a new X509 certificate; set to NULL on entry and on failure. pkey_out Receives the matching EVP_PKEY; set to NULL on entry and on failure.
- Returns
- 0 on success, -1 on any OpenSSL error.
- Note
- The key is P-256 (NID_X9_62_prime256v1). The certificate has version 3 (v2 encoding), serial 1, a 30-day validity starting now, and CN "cwist-webrtc". On failure all intermediate objects are freed and both outputs remain NULL; on success ownership moves to the caller, who must free them with X509_free()/EVP_PKEY_free().
Definition at line 36 of file dtls.c.
References cap, and EVP_sha256.
