#include <openssl/ssl.h>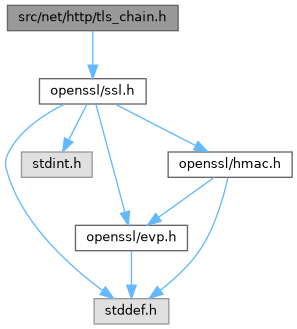
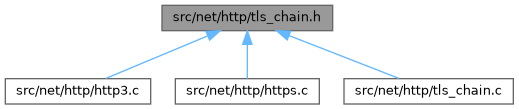
Go to the source code of this file.
Functions | |
| int | cwist_tls_autoload_intermediates (SSL_CTX *ssl_ctx) |
| Autoload missing intermediate CA certificates into an SSL_CTX chain. | |
| unsigned long | cwist_tls_sess_cache_size (void) |
Function Documentation
◆ cwist_tls_autoload_intermediates()
Autoload missing intermediate CA certificates into an SSL_CTX chain.
Starting from the current chain tail, walks up the issuance path using AIA caIssuers URLs until a self-signed (root) certificate is reached, the chain depth limit (CWIST_AIA_MAX_CHAIN_DEPTH) is hit, or no issuer can be fetched. Issuers that would duplicate a certificate already installed are not added.
- Parameters
-
ssl_ctx SSL context whose certificate chain should be completed.
- Returns
- number of intermediate certificates added (0 if none were needed or found), or -1 on error.
Definition at line 568 of file tls_chain.c.
References cap, and CWIST_AIA_MAX_CHAIN_DEPTH.
◆ cwist_tls_sess_cache_size()
Bounded retention for the BoringSSL server-side session cache.
BoringSSL's implicit cap is 20k entries per SSL_CTX (ssl.h SSL_SESSION_CACHE_MAX_SIZE); nothing in CWIST called SSL_CTX_sess_set_cache_size, so a deployment seeing TLS 1.2 session-ID resumption could accumulate up to that per worker process with no bound it could tune. The knob caps the cache on every server context. Measured session-cache usage under wrk/ab/h2load and openssl s_client TLS 1.2 churn is 0 (TLS 1.3 tickets are stateless and never enter the server cache), so today this is retention hardening, not an RSS win. The cap is consulted on session insert only: zero hot-path impact.
- Returns
- The validated CWIST_TLS_SESS_CACHE_SIZE env override or 1024; cached after first read. 0 leaves the BoringSSL default uncapped.
Definition at line 537 of file tls_chain.c.
References cap.
